Agenda Day 2
The agenda for the Secure AI Summit 2026 focused on the practical challenges of securing enterprise AI, co-located with the 4th annual Responsible AI Summit.
Day 2 Morning Sessions
7:00 am - 7:30 am
Secure AI & RAI Run Club
8:30 am - 9:15 am
Breakfast and Registration
9:15 am - 9:30 am
Chair's Opening Remarks
9:30 am - 10:00 am
Opening Panel Discussion – Shadow AI: The Unseen Attack Surface
Eric Martinez Cancela -
CISO,
Serunion
Robin Schoss - Head of Information Security and AI Governance, Olympus
Sheikh Mahbub Habib - Head of Product Cybersecurity and Privacy Innovation, AUMOVIO
The term "Shadow AI" is used everywhere, but often without precision. It is not just unsanctioned use of public tools. It spans a spectrum, from casual employee usage to internally built applications calling external model APIs, to semi-approved experiments that never pass through full governance. Some of it is visible, some of it is tolerated, and some of it is completely unknown. What matters is not the label but the condition: AI capability operating without clear oversight, consistent controls, or full visibility. This panel focuses on making that condition manageable and on where Shadow AI actually sits in the enterprise, how to detect it in practice, and how to bring it under control without slowing delivery or relying on bans that do not work.
10:00 am - 10:30 am
Presentation / Case Study – EBRD's Approach to Secure Innovation
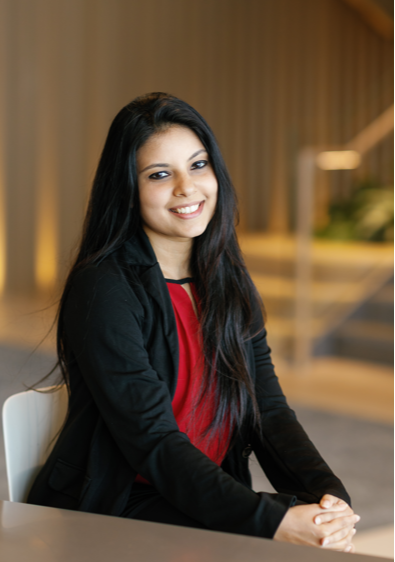
Abantika Chatterjee -
Head of AI Capability,
EBRD
James Jackson - AI Security Lead, EBRD
In this case study, Abantika Chatterjee, Associate Director, Head of AI Capability, EBRD, shares how the bank established its AI Centre of Excellence, vision, strategy and operating model from the ground up, bringing together business, technology, governance, and security teams to support innovation at scale. James Jackson, AI Security Lead, EBRD, then examines the cyber security challenges associated with deploying new AI capabilities, developed in-house or procured off-the shelf, and the approaches being taken to identify, manage, and mitigate emerging threats. Together, they offer practical lessons on embedding security into AI programmes from day one rather than operating in silos.
• Building an AI Centre of Excellence from the ground up.
• Embedding security into AI operating models from day one.
• Addressing cyber risks across emerging AI capabilities and tools.
10:30 am - 11:00 am
Morning Networking Coffee Break
Day 2 Late Morning Sessions
11:00 am - 11:45 am
Panel Discussion – AI Security: Standards, Policy & EU Enforcement Reality
Dimitris Tsapogas -
Global Head of Privacy and Data Protection,
DHL Supply Chain
Michael Gerhard Schneider - Principal Expert Product Cybersecurity & Privacy, AUMOVIO
Zahra Zohoor - Business Security & Resilience Officer, Nationwide Building Society
Hannah Liu - Research Engineer, AI Policy and Governance, Responsible AI Institute
Standards for AI are moving quickly. The EU AI Act, NIST frameworks, and Cyber Resilience Act are starting to define expectations. But inside most organisations, these standards have not yet been translated into clear internal rules or enforceable controls. At the same time, agentic AI introduces systems that act, decide, and adapt in ways those standards only partially address. This panel focuses on the gap between policy and practice. It addresses how to turn emerging standards into something usable, define what is acceptable inside your organisation, and evidence control when regulators ask.
11:45 am - 12:30 pm
Presentation / Case Study: Poisoned Pipelines: Securing AI Infrastructure Against Supply Chain Attacks
Luigi Renna -
Director of Security Architecture,
Barclays
The rush to build AI-enabled applications has created a new software supply chain risk surface, with attackers increasingly targeting the open-source ecosystems powering modern AI development. Recent npm incidents in the AI space have exposed how quickly compromised tooling can spread through developer environments and production systems. In this session, Director of Security Architecture at Barclays explores what these attacks reveal about the intersection of application security and AI security, why existing security practices are struggling to keep pace, and how organisations can better anticipate, detect, and reduce emerging supply chain threats before they scale across the enterprise.
Day 2 Lunch
12:30 pm - 1:30 pm
Networking Lunch
Day 2 Afternoon Sessions
1:30 pm - 2:00 pm
Presentation - Talk Details to be Announced
Agnes Bade -
Vice President Group Head AI & Digital Law,
The Adecco Group
2:00 pm - 2:30 pm
Inside the Attacks: Lessons on Securing LLMs and Agentic AI
Ioannis Agrafiotis -
Senior Research Associate and Expert in Capacity Building,
European Union Agency for Cybersecurity (ENISA)
As organisations rapidly deploy LLMs and agentic AI systems, attackers are discovering new ways to exploit them. In this session, Ioannis Agrafiotis, Senior Research Associate at the University of Oxford and former cybersecurity expert at the European Union Agency for Cybersecurity (ENISA), will explore the most significant security threats facing AI today, drawing on real-world incidents including the EchoLeak attack targeting Microsoft Copilot and the compromise of McKinsey's Lilli AI assistant. Through audience discussion and practical case studies, the session will examine how these attacks work, the risks they expose, and the controls needed to build secure and resilient AI systems.
• Understanding emerging attacks against LLMs and AI agents.
• Addressing critical AI governance and security risks.
• Applying practical controls for secure AI deployment.
Ioannis Agrafiotis
Senior Research Associate and Expert in Capacity BuildingEuropean Union Agency for Cybersecurity (ENISA)
2:30 pm - 3:00 pm
Closing Panel Discussion – From Threat Talk to Boardroom Buy-In: Making AI Security a Business Enabler
Manish Gupta -
Head of Cyber Security for Europe,
Ericsson
Dimitris Tsapogas - Global Head of Privacy and Data Protection, DHL Supply Chain
"No news is good news" has long defined security success, but AI, especially agentic systems, has changed the reality. Risk is now continuous, visible and shaped by autonomous behaviours that require constant oversight. As boards push to accelerate AI adoption, confidence depends on proving it can be done securely. This panel explores how security leaders can reposition AI security from a perceived blocker to a strategic enabler of trust, investment and business value.